
 MONA OS 2.0
 Partner with MONA


 Tự động hoá doanh nghiệp
 Cẩm nang SEO
 Digital Marketing
 Kinh nghiệm thiết kế website
 Hạ Tầng Server
 Giáo dục


 VI
 EN









Message us on
Zalo Official


 ProductsNew

 ProductsProducts
 Mới ra mắtKHA AI 2027App tự edit video, tự đăng mọi mạng xã hội, 2 phút mỗi ngày










 Website designLooks good and wins customers over.
SEO servicesBrings in customers searching for exactly what you sell.
 Tư vấn digital marketingKéo khách từ nhiều kênh, đo bằng số thật.
Corporate video productionVideos introducing your company, factory and team.
 NewAI video productionCompany story films made with AI.
 Custom software developmentCRM, ERP and HRM built for your business.
 Viết AI Agent theo yêu cầuĐặt riêng một trợ lý AI cho đúng việc của mình.
 Tư vấn chuyển đổi AIĐưa AI vào vận hành của cả công ty.
NewMONA LMSManagement for centers and schools.
MONA SkillHubInternal training for company staff.
 NHTQ systemEnd-to-end China–Vietnam shipping operations.
MONA JMSManagement for gold, diamond and pawn shops.
 MONA E-LearningA website with every feature you need to sell courses.
 How to sell online courses (course)More than 30 free lessons on selling courses on autopilot.
 MONA Cloudmonacloud.vnServers to get your apps and websites running.
 MONA Basemonabase.vnPostgres database, sign-in and file storage.
 MONA Mailmonamail.vnSend OTP, order and invoice emails from your software.
 MONA Paymonapay.vnAccept bank transfers via VietQR and notify your software when the money arrives.
 MONA eInvoiceComing soonIssue e-invoices that meet tax standards.
Gấu CườiTrả lời khách 24/7 trên web, Fanpage, Zalo và thu lead cho sale.
 Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Dê CườiTư vấn và chốt đơn cho shop ngay trong khung chat.
Gấu WebmasterNhắn nhóm Zalo là website được sửa xong.
 Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
 Gấu Báo GiáLên báo giá đúng mẫu và gửi khách ngay.
 AI chăm sóc khách hàngTheo dõi và giữ chân khách hàng cũ.
 Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên.
 Mới ra mắt
KHA AI 2027
Xây kênh chuyên gia 2 phút mỗi ngày
Quay bằng điện thoại, AI tự edit video, tự đăng lên 16 nền tảng và tự trả lời bình luận, tin nhắn.
912.198lượt xem trên kênh CEO MONA sau 38 ngày
 Anh Khánh HùngCEO MONA đang dùng mỗi ngày
Xem app làm được gì
 AI
Gấu Cười MONA ĐANG TỰ XÀITrả lời khách 24/7 trên website, Zalo OA, Messenger và thu lead về cho sale.
Dê CườiChốt đơn bán lẻ và sàn: Shopee, TikTok Shop, web. Chăm cả khách sỉ, đại lý.
Gấu WebmasterCập nhật nội dung, tối ưu SEO website mỗi ngày.
Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên tự động.
AI chăm sóc khách hàngGiữ khách cũ, cứu lead đã rớt cho phòng kinh doanh.
Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
Gấu Báo GiáLên báo giá đúng mẫu, gửi khách ngay khi có yêu cầu.
 Chuyển đổi AI toàn phầnGiải pháp tổng cho doanh nghiệp, 3 lớp triển khai.
 Viết AI Agent theo yêu cầuĐặt riêng một con AI gánh đúng nghiệp vụ của bạn.
 Custom softwareCRM, ERP and HRM with built-in AI automation.
 SEO & AEO thời đại AIĐược Google lẫn AI trích dẫn, không chỉ xếp hạng.
 Kiến thức AI cho doanh nghiệpBài phân tích, hướng dẫn ứng dụng AI vào vận hành.
 Free AI courses
 AI tools at work
App mới · KHA AI 2027
Xây kênh 2 phút mỗi ngày
AI tự edit video, tự đăng mọi mạng xã hội
Free consultation, 8am–10pm every day

18 March, 2023
What is CIDR? CIDR (full name Classless Inter-Domain Routing) is a method introduced in 1993 to improve the allocation of an IP address and slow the exhaustion of IPv4 address resources. How do CIDR addresses work, and how is CIDR used in networks? Let's look at it in detail in the article below.

CIDR (Classless Inter-Domain Routing) is one of the methods that supports the allocation and routing of IP addresses. It was introduced in 1993 to overcome the limits of an IP address based on classes and to limit the exhaustion of IPv4 address resources.
Example: A business has 8 class C addresses: 200.100.48.0/24 – 200.100.55.0/24
In a full IPv4 network design, the network prefix is one or more groups of 8 bits, which leads to class A, B and C address blocks. Classless inter-domain routing does not allocate address space to Internet service providers and end users on any address bit boundary.
In IPv6, however, the interface identifier has a fixed size of 64 bits by convention, and smaller subnets are never allocated to end users.
-> See more: Overview of the IPv4 and IPv6 protocols
Now that you know what CIDR is, let's look at what CIDR does and how it is used. In detail:
To understand how CIDR works, you also need to know about CIDR blocks and CIDR notation, covered next.

CIDR blocks are groups of addresses that share the same prefix and contain the same number of bits. Several connected CIDR blocks can be combined into a larger system that shares a common network prefix, which is what supernetting is. The size of a CIDR block is determined by the length of its prefix:
The initial blocks are handled by the number-assignment authority Internet (IANA, the Internet Assigned Numbers Authority). IANA is responsible for distributing large blocks of IP addresses to the Regional Internet Registries (RIRs). These blocks serve large regions such as Africa, North America and Europe.
When an RIR receives a block, it creates smaller blocks to assign to Local Internet Registries (LIRs).
CIDR blocks can be split further until they reach the end user. The size of the block an end user gets depends largely on how many individual addresses they need.
Most end users are assigned blocks by their Internet service providers. Organizations that want an independent block, however, need to go through an ISP to get one from authorities such as an LIR or RIR.
-> See more: Overview of ICANN (Internet Corporation for Assigned Names and Numbers)
Some IP addresses are reserved for special purposes. For example, the Class B range 192.168.0.0 is fixed and cannot be changed, and it is used to identify private networks. Most home broadband routers assign these network addresses 192.168… to the devices in the home.
CIDR also does not allow a host identifier of all zeros, and it reserves the all-ones identifier to work as a broadcast address: data packets sent to this address are forwarded to every host on the network.
Originally, IP addresses were assigned in the main address classes A to C. Each class takes a different part of the 32-bit IP address to identify the gateway router for the packet: the first 8 bits for Class A, the first 16 for Class B and the first 24 for Class C. The bits not used for the network identifier are available to identify hosts on that network.
In a CIDR IPv4 address, the 32-bit address is split into four groups of 8 bits, each called an octet. The four groups look like this:
CIDR notation is compact. It gives the network mask for an address by adding the number of network bits after a "/". For example: 192.168.129.23/17 gives you a 17-bit network mask. Internet users can refer to the whole network as A/17 to indicate its size without spelling out the actual network mask.

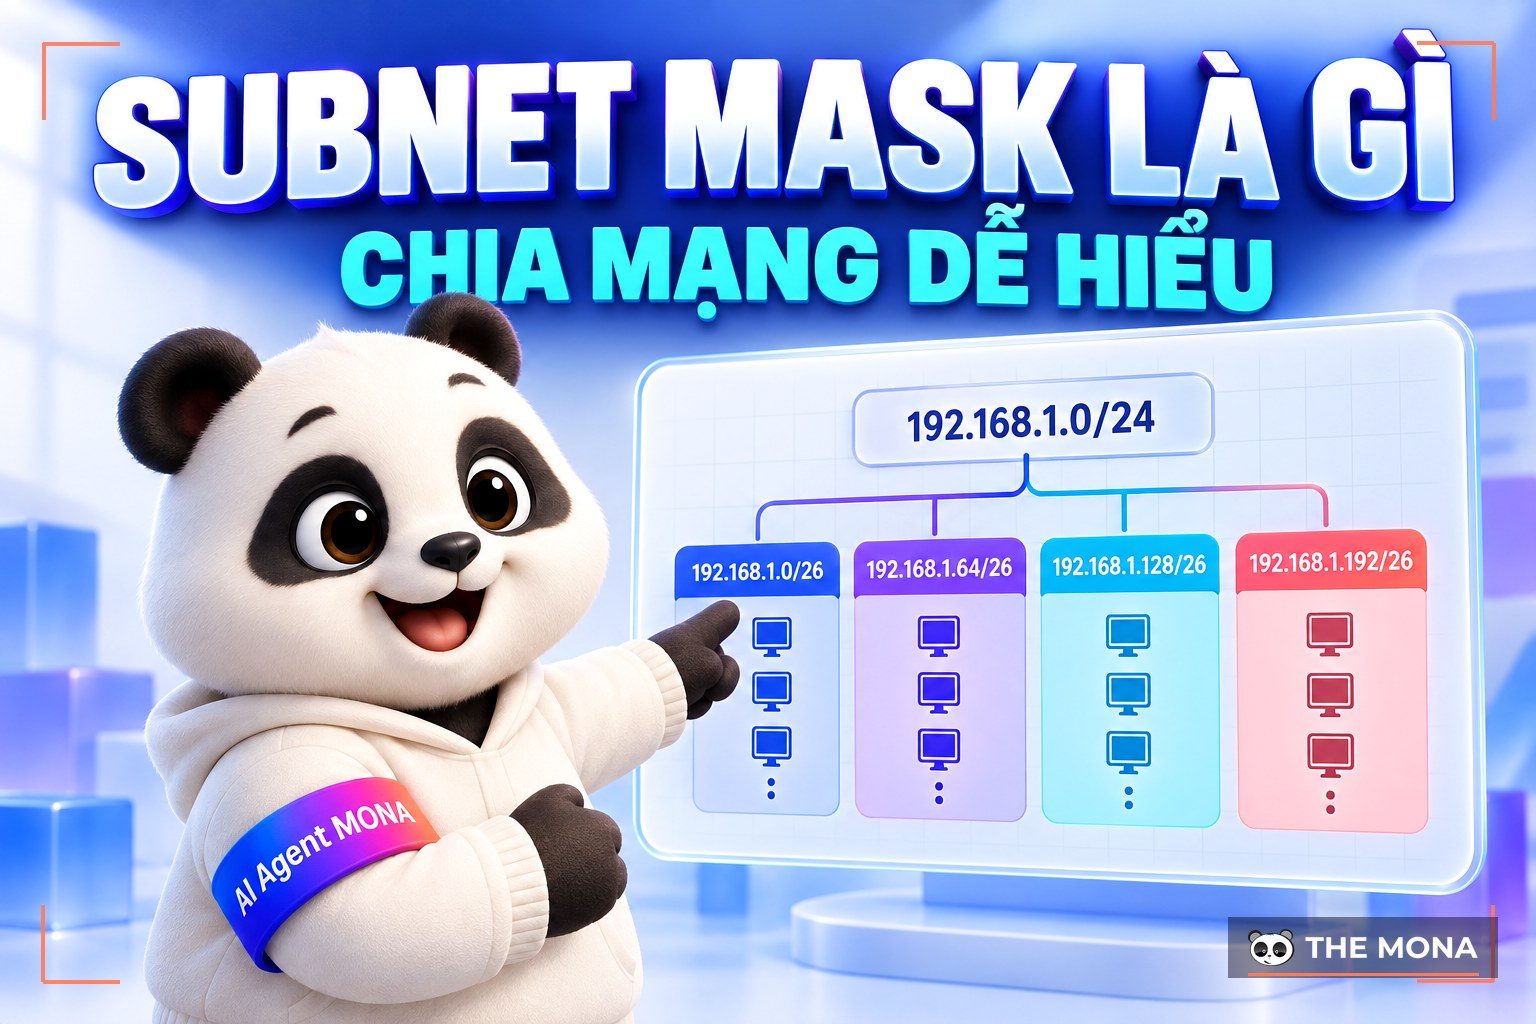
CIDR is built on VLSM (Variable Length Subnet MaskSubnet Masking), a technique that lets engineers divide an IP address space into subnets of different sizes. It creates subnets with different numbers of hosts without wasting large numbers of addresses. It defines prefixes of arbitrary length, which makes it more efficient than the earlier system.
In addition,Classless Inter-Domain Routing can also aggregate several standard classful networks into one larger network. This reduces the number of entries in a router's routing table and increases the number of hosts allocated in the network without needing the network ID of a higher class.
A router using CIDR uses the destination address to route a packet toward the gateway destination (network node), and then resolves the address based on what it knows about the details of the supernetwork (supernet). If some routers know routes for different parts of the same supernet, it uses the longest matching network prefix.
CIDR has reduced the waste of IPv4 addresses without causing the number of routing table entries to explode. It allows a single routing table entry for a supernet to represent a set of networks, so only the router closest to the actual destination needs to know the detailed routes.
CIDR is now part of the routing system in the core of the Internet, and every ISP can use it. It is supported by the Border Gateway Protocol (BGP), as well as common protocols such as Exterior Gateway Protocol and Open Shortest Path First (OSPF).
CIDR is used when an organization or service provider manages addresses for a large number of hosts or networks. It should use supernetting together with Network Address Translation (NAT) to allocate address ranges in a way that makes traffic handling more efficient.
For example, you can use supernetting to split an internal network into subnets for administrative purposes, so that each department manages its own address space.
Classless Inter-Domain Routing is used in IPv6 to manage address allocation and routing tables. In IPv6, CIDR works much as it does in IPv4, with a few small differences.
In IPv6, an IP address is a 128-bit address divided into 16-bit blocks called "hextets".
In short, CIDR notation in IPv6 helps manage IP address allocation and subnetting by specifying the number of prefix bits of the IPv6 address.

Before CIDR, IP addresses were usually allocated by class. With this older method, IPv4 addresses were at risk of running out quickly. The routing system had three separate classes: A, B and C. Of these:
When a business needs more than 254 hosts, it runs into problems. It no longer fits in Class C and falls into Class B instead, so the business has to use a Class B allocation even if it needs far fewer than 65,535 host identifiers.
So a business holding a Class B allocation has to accept wasting a large number of hosts, which significantly reduces the availability of IPv4.
Can CIDR blocks overlap?
Yes. CIDR blocks can overlap when IP addresses are divided and used. When two or more CIDR blocks overlap, IP address conflicts can occur.
This can cause routing problems and make it hard to send and receive data for the overlapping addresses. So when you divide a network into CIDR blocks, make sure the blocks do not overlap.
How do you use IP addresses efficiently with CIDR?
To use IP addresses efficiently with CIDR, use smaller CIDR blocks and allocate only the number of IP addresses each subnet needs. This avoids wasting unused addresses and lets you divide them more flexibly among specific subnets.
Are CIDR and subnetting different?
CIDR and subnetting are related concepts in dividing IP addresses within a network. Classless Inter-Domain Routing is a method of dividing IP addresses without the old classful system, while subnetting is the process of dividing a large network into smaller subnets.
This article by Mona Media We hope this has given you a clearer picture of what CIDR is and how it works. CIDR is a method of allocating addresses and routing IP traffic. It was created to overcome the limits of class-based IP allocation and to slow the exhaustion of IPv4 address resources.

CEO & Founder · The MONA
Founder of The MONA, who built a services company of 60+ staff with 14,000+ projects delivered. Khánh Hùng shares how he thinks about building systems that run themselves, automating a business, and the real lessons from delivering projects at MONA.
 1,5K




Professional website
design services
Own a website with a beautiful, 100% exclusive design and a lifetime warranty, with the ability
to expand features flexibly as your business grows, starting today!






 MONA will never sell your information or send you spam


 MONA will never sell your information or send you spam
