
 MONA OS 2.0
 Hợp tác với MONA


 Tự động hoá doanh nghiệp
 Cẩm nang SEO
 Digital Marketing
 Kinh nghiệm thiết kế website
 Hạ Tầng Server
 Giáo dục


 VI
 EN












Message us on
Zalo Official


 ProductsNew

 ProductsProducts
 Mới ra mắtKHA AI 2027App tự edit video, tự đăng mọi mạng xã hội, 2 phút mỗi ngày










 Thiết kế websiteVừa đẹp vừa thuyết phục được khách.
Dịch vụ SEOKéo về khách đang tìm đúng thứ anh chị bán.
 Tư vấn digital marketingKéo khách từ nhiều kênh, đo bằng số thật.
Quay video doanh nghiệpVideo giới thiệu công ty, nhà xưởng, đội ngũ.
 MớiDựng video AIDựng phim câu chuyện công ty bằng AI.
 Custom software developmentCRM, ERP and HRM built for your business.
 Viết AI Agent theo yêu cầuĐặt riêng một trợ lý AI cho đúng việc của mình.
 Tư vấn chuyển đổi AIĐưa AI vào vận hành của cả công ty.
NewMONA LMSManagement for centers and schools.
MONA SkillHubInternal training for company staff.
 NHTQ systemEnd-to-end China–Vietnam shipping operations.
MONA JMSManagement for gold, diamond and pawn shops.
 MONA E-LearningA website with every feature you need to sell courses.
 How to sell online courses (course)More than 30 free lessons on selling courses on autopilot.
 MONA Cloudmonacloud.vnServers to get your apps and websites running.
 MONA Basemonabase.vnPostgres database, sign-in and file storage.
 MONA Mailmonamail.vnSend OTP, order and invoice emails from your software.
 MONA Paymonapay.vnAccept bank transfers via VietQR and notify your software when the money arrives.
 MONA eInvoiceComing soonIssue e-invoices that meet tax standards.
Gấu CườiTrả lời khách 24/7 trên web, Fanpage, Zalo và thu lead cho sale.
 Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Dê CườiTư vấn và chốt đơn cho shop ngay trong khung chat.
Gấu WebmasterNhắn nhóm Zalo là website được sửa xong.
 Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
 Gấu Báo GiáLên báo giá đúng mẫu và gửi khách ngay.
 AI chăm sóc khách hàngTheo dõi và giữ chân khách hàng cũ.
 Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên.
 Mới ra mắt
KHA AI 2027
Xây kênh chuyên gia 2 phút mỗi ngày
Quay bằng điện thoại, AI tự edit video, tự đăng lên 16 nền tảng và tự trả lời bình luận, tin nhắn.
877.623lượt xem trên kênh CEO MONA sau 35 ngày
 Anh Khánh HùngCEO MONA đang dùng mỗi ngày
Xem app làm được gì
 AI
Gấu Cười MONA ĐANG TỰ XÀITrả lời khách 24/7 trên website, Zalo OA, Messenger và thu lead về cho sale.
Dê CườiChốt đơn bán lẻ và sàn: Shopee, TikTok Shop, web. Chăm cả khách sỉ, đại lý.
Gấu WebmasterCập nhật nội dung, tối ưu SEO website mỗi ngày.
Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên tự động.
AI chăm sóc khách hàngGiữ khách cũ, cứu lead đã rớt cho phòng kinh doanh.
Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
Gấu Báo GiáLên báo giá đúng mẫu, gửi khách ngay khi có yêu cầu.
 Chuyển đổi AI toàn phầnGiải pháp tổng cho doanh nghiệp, 3 lớp triển khai.
 Viết AI Agent theo yêu cầuĐặt riêng một con AI gánh đúng nghiệp vụ của bạn.
 Custom softwareCRM, ERP and HRM with built-in AI automation.
 SEO & AEO thời đại AIĐược Google lẫn AI trích dẫn, không chỉ xếp hạng.
 Kiến thức AI cho doanh nghiệpBài phân tích, hướng dẫn ứng dụng AI vào vận hành.
 Free AI courses
 AI tools at work
App mới · KHA AI 2027
Xây kênh 2 phút mỗi ngày
AI tự edit video, tự đăng mọi mạng xã hội
Free consultation, 8am–10pm every day

26 September, 2026

In September 2026 alone, we had to clean up 12 websites infected with malware. What all of these projects had in common was an administrator leaving the server's network ports wide open. What is a firewall? A firewall is a security system that sits between your network and the internet. Its job is to inspect all data passing through the network connection. The system decides whether to allow or block data based on the rules you set. You only need to set up these traffic rules correctly. The server will then automatically avoid most of the scans run by hackers' tools.
A firewall is a network security barrier. At MONA we like to compare it to the ticket checkpoint at an airport gate. Every passenger must show a valid ticket to pass through. A network server works exactly the same way. We often tell customers: a firewall only decides who may knock on the door, while killing viruses is a different job.
Data on the internet travels in small packets. A firewall strips off the outer layer of each packet to inspect it. It checks the source network address of the incoming traffic. It also checks the destination address on the server. This inspection runs continuously, every second, on every network connection.
If a packet is valid under the rules, the system lets it through right away. If it detects a risk, the firewall blocks it and discards the packet at the edge of the network. This inspection keeps malware from getting into your server. Conversely, it also stops sensitive data from being quietly smuggled out to the internet by hackers.
A network without a firewall is like a house with every door open. Anyone on the internet can probe and connect straight to the open ports. A firewall lets you hide the ports that don't serve users. Attackers can't see the weak points they would need to steal your data.
It doesn't only keep strangers out. It also controls the programs running inside the operating system. When malware slips into a server, it tries to phone home to the hacker's server. A properly configured firewall blocks that outbound traffic.
Firewalls are usually divided into two main groups: hardware and software. We see many people working on personal projects wonder which kind to buy. In practice, each type solves a different security problem for a different network.
A hardware firewall is a standalone physical device. Picture a network box plugged straight into the fiber cable. All network signals from outside must pass through this box before reaching the servers inside.
The device has its own processor dedicated to analyzing network packets. That way, the main server doesn't spend resources on filtering data. Large financial groups often buy hardware to protect hundreds of computers at once. The one drawback is that the equipment is usually very expensive. Configuring it also requires a network engineer with deep operating expertise.
A software firewall is a program installed right on the operating system of your VPS. This kind of security doesn't require you to spend money on extra physical hardware. Linux and Windows servers both come with built-in network management software. You only need to type a few commands in the terminal to turn it on right away.
It filters data at the gateway of the operating system kernel. It is extremely flexible, and its rules are easy to change for each specific project. Ordinary web applications only need a software firewall to reach a safe standard. However, this software shares part of the host server's CPU and RAM to process its rules.
| Criterion | Hardware firewall | Software firewall |
|---|---|---|
| The practice of | A physical hardware device | An application installed on the operating system |
| Cost | Requires a high upfront investment | Usually free with the operating system |
| Placement | Sits between the internet cable and the network | Installed directly on each server |
| Processing performance | Uses a dedicated network processor | Shares the VPS's CPU and RAM |
| Best for | Large, expanding business networks | Personal hosting servers and web applications |
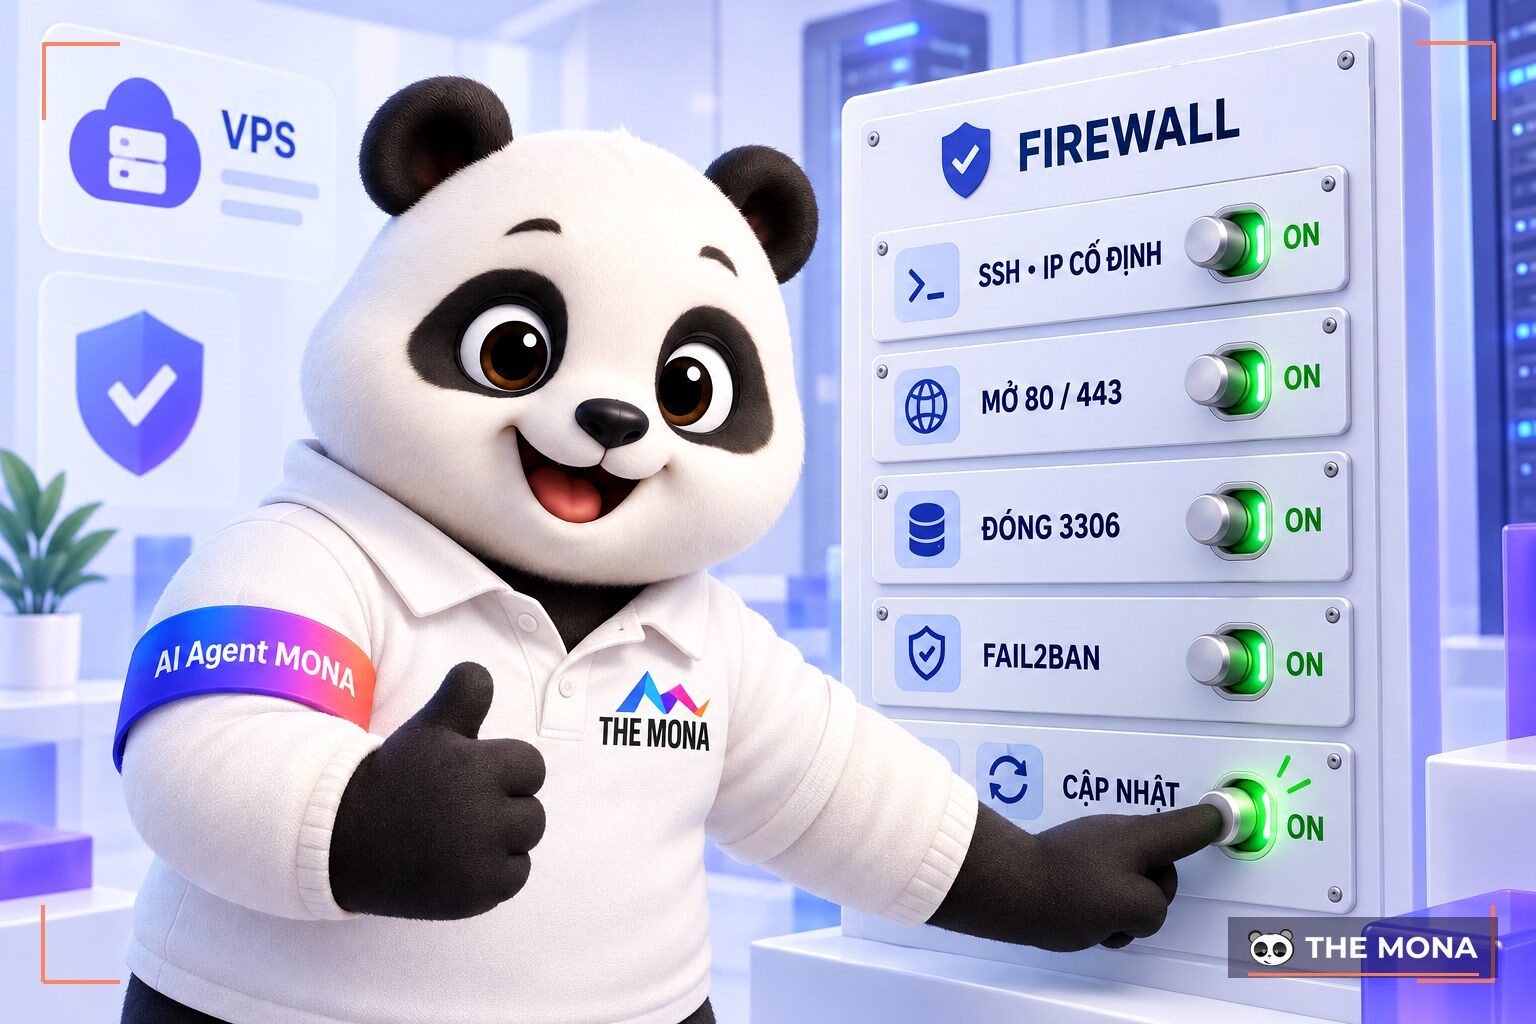
A firewall works according to rules that people configure in advance. We often advise developers to understand how these rules take priority over one another, to avoid locking themselves out of the server.
The system always reads the rule list in priority order, from top to bottom. Each service on the server is assigned its own communication port. Port 80 is typically used to show the website in an outside browser. Port 22 is used by default for technicians to connect to the admin console.
When traffic arrives, the firewall takes the destination port and matches it against the rules. Say you order a block on unknown IP addresses connecting to port 22. The firewall slams the connection shut from the very first second. Say you allow everyone on the network to reach port 80. The firewall opens the way so visitors can load the website normally.
These rules can be adjusted flexibly by IP address or application domain. Experienced administrators always start with a rule that blocks the whole network. Only then do they open, one by one, the ports that are really needed. This passive defense method gives the platform a very high level of safety.
Newer firewalls also add filtering by connection state. The system keeps a history of the connections of users working on the web. If a stray packet arrives that doesn't belong to an existing conversation, it is dropped immediately. To learn more about protecting web infrastructure, you can look at WordPress website security methods and plugins. The firewall protects the outer ring, while plugins keep the inner ring of the source code safe.
Today's computing infrastructure offers many firewall tools to protect a system. At MONA, we often combine several layers of software to keep customer data safe. Understanding what each tool does will help you assign your layers of defense sensibly.
UFW (Uncomplicated Firewall) is a network management tool built into Ubuntu. UFW was designed to simplify otherwise complicated network configuration commands. A developer only needs to type one short command to close or open a network port. It is very friendly to people just learning basic Linux system administration.
iptables is the core packet filter that sits deep in the operating system kernel. It controls the network in fine detail, but its command syntax is long and hard to remember. UFW is really just a wrapper that makes it easier to drive the iptables process. Network specialists often prefer writing iptables rules directly to tune network parameters in depth.
A WAF (Web Application Firewall) is a firewall designed specifically for running websites. UFW and iptables can only block network traffic by IP address or port. A WAF can read and understand the content of web traffic reaching the server. It detects JavaScript malicious code being injected into login forms. It also stops queries deliberately written to damage the database.
WAF solutions are usually offered by infrastructure platforms such as Cloudflare to protect application bandwidth. This layer blocks millions of junk requests meant to take a website down. Many businesses also combine a WAF with a VPN architecture to grant staff secure access.
A freshly created VPS is always facing a wave of automated scanners. We advise developers to set up the following 5 defensive rules right after receiving the server details. These steps take only a few minutes but give your application a lasting safety barrier.
The first rule is to open only the ports that directly serve your software. An ordinary website only needs port 80 (HTTP) and port 443 (HTTPS) to deliver content. Every other service port must stay closed. Closing unneeded ports reduces your platform's attack surface as much as possible.
Second, change the system administration (SSH) port right away. Attackers constantly run automated scans against the server's default port 22. Moving to a large random number breaks the script of those scanning tools. Your server will no longer be pestered by thousands of password-guessing attempts a day.
Third, block traffic by region or by suspicious IP address. A software project that only sells in Vietnam has no reason to accept traffic from distant countries. Set rules that block unfamiliar regions to remove the risk of malware attacks. Using a proxy server can sometimes hide the real visitor IP address. The firewall then needs extra configuration to read the real IP behind the proxy.
Fourth, turn off all software that runs in the background but isn't used. If a service isn't running, the operating system won't open extra network ports to the outside. The leaner the platform, the lower the chance of a system vulnerability appearing by accident.
Finally, keep access logs that trace the whole system. Every decision to block a network packet should be carefully recorded in a text file by the software. With this log data, technicians can review the traces of an attack when a risk alert comes in.
When you rent and manage a traditional VPS yourself, network configuration often slows a developer's work. At MONA we build hosting solutions designed specifically for developers. The system automatically handles many complex network protection steps so you can spend your time writing code. We cleaned up 12 websites infected with malware in September 2026, mostly because the servers had unnecessary ports open.
The MONA Cloud infrastructure offers servers on a flexible pay-for-resources model. Rental is billed by the hour of use, starting from just 550 VND per hour for a small server. All service fees are paid directly in VND, with a full VAT invoice each month. You have complete control to turn the server on or off based on your actual testing needs. Once the system receives a shutdown command, CPU and RAM charges stop completely.
Getting your code into a live environment is extremely fast. Creating a new VPS takes just 11 seconds. App host configuration that issues an HTTPS certificate takes about 150 seconds. The platform runs very stably thanks to data infrastructure spread across 5 regions, from Vietnam to the US. Environments in Vietnam, Hong Kong or Singapore give very fast response times to local visitors.
Development teams can easily push code to the network through the built-in CLI. Engineers using AI can also work directly through the modern MCP standard. The MCP toolset connects the MONA infrastructure straight to Claude Code or Codex to control network commands automatically. The platform comes with network security configuration docs with detailed steps for setting up a firewall for your application platform.
Right now, every newly created customer account is MONA Cloud given 100,000 VND in credit added to its payment wallet. This trial budget is worth 180 hours of running a server at the standard configuration. You can use this credit to create a VPS right away and practice setting up network protection rules early.
A firewall is a filtering layer that blocks malicious traffic from entering an internal network. Configuring a firewall is a mandatory operating step for any server that holds important databases. It creates an outer security barrier that stops hackers from trying to take control.
You need to log in with an account that has server administrator privileges to run the command that changes its state. The command ufw disable turns off the packet-blocking mechanism running on an Ubuntu server. Turn this mechanism off only briefly, to fix a software connection problem.
A hardware firewall is a physical device completely separate from the main server. It uses its own chip to handle large volumes of network data smoothly. A software firewall, by contrast, is a program installed on the operating system of the server itself. It shares the CPU and RAM with other services.
You should run both layers of network protection on your application. UFW blocks the unneeded ports of the operating system environment. A WAF running alongside it analyzes incoming content to filter out sophisticated malicious code.

CEO & Founder · The MONA
Founder of The MONA, who built a services company of 60+ staff with 14,000+ projects delivered. Khánh Hùng shares how he thinks about building systems that run themselves, automating a business, and the real lessons from delivering projects at MONA.
 443




Professional website
design services
Own a website with a beautiful, 100% exclusive design and a lifetime warranty, with the ability
to expand features flexibly as your business grows, starting today!






 MONA will never sell your information or send you spam


 MONA will never sell your information or send you spam
