
 MONA OS 2.0
 Partner with MONA


 Tự động hoá doanh nghiệp
 Cẩm nang SEO
 Digital Marketing
 Kinh nghiệm thiết kế website
 Hạ Tầng Server
 Giáo dục


 VI
 EN













Message us on
Zalo Official


 ProductsNew

 ProductsProducts
 Mới ra mắtKHA AI 2027App tự edit video, tự đăng mọi mạng xã hội, 2 phút mỗi ngày










 Website designLooks good and wins customers over.
SEO servicesBrings in customers searching for exactly what you sell.
 Tư vấn digital marketingKéo khách từ nhiều kênh, đo bằng số thật.
Corporate video productionVideos introducing your company, factory and team.
 NewAI video productionCompany story films made with AI.
 Custom software developmentCRM, ERP and HRM built for your business.
 Viết AI Agent theo yêu cầuĐặt riêng một trợ lý AI cho đúng việc của mình.
 Tư vấn chuyển đổi AIĐưa AI vào vận hành của cả công ty.
NewMONA LMSManagement for centers and schools.
MONA SkillHubInternal training for company staff.
 NHTQ systemEnd-to-end China–Vietnam shipping operations.
MONA JMSManagement for gold, diamond and pawn shops.
 MONA E-LearningA website with every feature you need to sell courses.
 How to sell online courses (course)More than 30 free lessons on selling courses on autopilot.
 MONA Cloudmonacloud.vnServers to get your apps and websites running.
 MONA Basemonabase.vnPostgres database, sign-in and file storage.
 MONA Mailmonamail.vnSend OTP, order and invoice emails from your software.
 MONA Paymonapay.vnAccept bank transfers via VietQR and notify your software when the money arrives.
 MONA eInvoiceComing soonIssue e-invoices that meet tax standards.
Gấu CườiTrả lời khách 24/7 trên web, Fanpage, Zalo và thu lead cho sale.
 Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Dê CườiTư vấn và chốt đơn cho shop ngay trong khung chat.
Gấu WebmasterNhắn nhóm Zalo là website được sửa xong.
 Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
 Gấu Báo GiáLên báo giá đúng mẫu và gửi khách ngay.
 AI chăm sóc khách hàngTheo dõi và giữ chân khách hàng cũ.
 Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên.
 Mới ra mắt
KHA AI 2027
Xây kênh chuyên gia 2 phút mỗi ngày
Quay bằng điện thoại, AI tự edit video, tự đăng lên 16 nền tảng và tự trả lời bình luận, tin nhắn.
915.115lượt xem trên kênh CEO MONA sau 39 ngày
 Anh Khánh HùngCEO MONA đang dùng mỗi ngày
Xem app làm được gì
 AI
Gấu Cười MONA ĐANG TỰ XÀITrả lời khách 24/7 trên website, Zalo OA, Messenger và thu lead về cho sale.
Dê CườiChốt đơn bán lẻ và sàn: Shopee, TikTok Shop, web. Chăm cả khách sỉ, đại lý.
Gấu WebmasterCập nhật nội dung, tối ưu SEO website mỗi ngày.
Gấu TeleSalesGọi điện tư vấn, chăm khách như tổng đài viên thật.
Gấu Tuyển DụngLọc hồ sơ, hẹn lịch, phỏng vấn ứng viên tự động.
AI chăm sóc khách hàngGiữ khách cũ, cứu lead đã rớt cho phòng kinh doanh.
Gấu Pháp ChếSoạn hợp đồng, rà điều khoản trong vài phút.
Gấu Báo GiáLên báo giá đúng mẫu, gửi khách ngay khi có yêu cầu.
 Chuyển đổi AI toàn phầnGiải pháp tổng cho doanh nghiệp, 3 lớp triển khai.
 Viết AI Agent theo yêu cầuĐặt riêng một con AI gánh đúng nghiệp vụ của bạn.
 Custom softwareCRM, ERP and HRM with built-in AI automation.
 SEO & AEO thời đại AIĐược Google lẫn AI trích dẫn, không chỉ xếp hạng.
 Kiến thức AI cho doanh nghiệpBài phân tích, hướng dẫn ứng dụng AI vào vận hành.
 Free AI courses
 AI tools at work
App mới · KHA AI 2027
Xây kênh 2 phút mỗi ngày
AI tự edit video, tự đăng mọi mạng xã hội
Free consultation, 8am–10pm every day

18 March, 2023
SSH, also called Secure Shell, is a protocol that lets users remotely control, manage and edit a server over the Internet. Secure Shell provides an algorithm to authenticate the user, passes input from the client to the host and returns the result to the client. It replaces the unencrypted Telnet program and uses cryptographic techniques so that all remote server activity is encrypted.
Secure Shell connects to the server and handles many functions in a control system, such as remote access to the system, secure file transfer, secure command execution and management of network infrastructure components. Its predecessor, Telnet, has fairly weak security, and SSH fixed that problem.
Most data centers have Secure Shell, and it ships with most Linux, Mac and Unix servers. A common use is connecting to an application to build a host system or a remote local machine, in order to make changes, upgrade and access the server automatically.
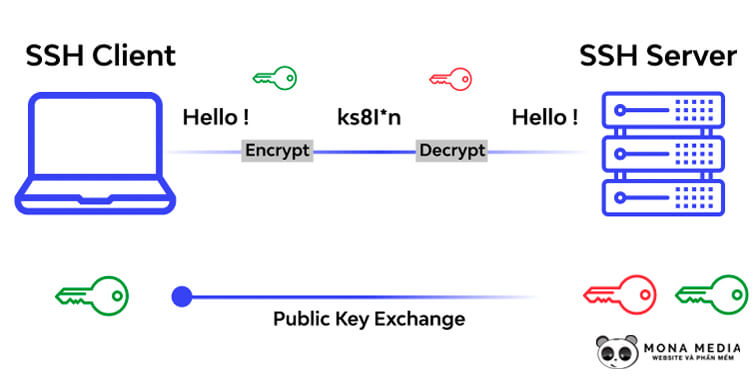
The SSH protocol uses a client-server model with a session, made up of several layers and types of encryption, allowing secure authentication between two remote devices. Secure Shell runs on TCP port 22 by default and starts a connection with the client by performing a TCP handshake with the server. Activity on the server after using Secure Shell is encrypted, ensuring a symmetric connection.
Secure Shell works in two basic parts: connection and authentication. Once the two remote devices are connected through the command line “ssh server.example.org”, the protocol compares the user's login details to verify the connection. Authentication in Secure Shell is mainly about hosts supporting each other. It works with terminal emulators, protocol applications and file transfers.
Users can save the host key for the next connection and authentication. It is a hidden file stored by default, so it is very safe from a security standpoint. If you need single sign-on (SSO), the protocol is an ideal choice. You can switch quickly between accounts without re-entering login details.
The main advantage of Secure Shell over earlier applications with similar functions is encryption. Users can transfer data between host and client with confidence.
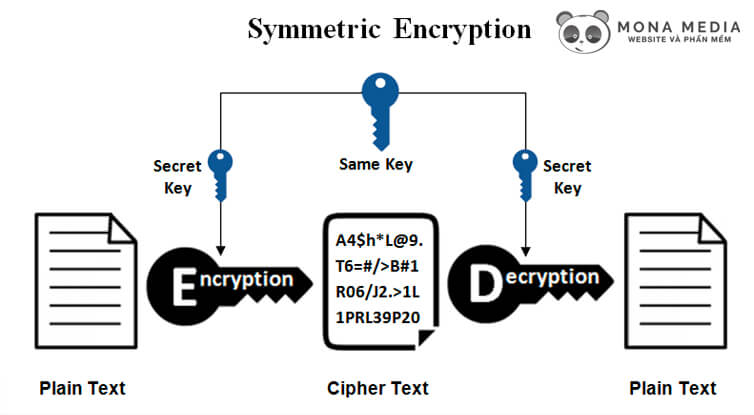
Symmetric encryption in Secure Shell is a two-way method using a secret key. Anyone who holds the key can decrypt messages for the host and client. It is widely used to encrypt sessions. The generated key must stay secret between the two parties and never be disclosed to a third party.
With symmetric encryption, both computers can share information with each other. Even if a third party intercepts the signal, they cannot decrypt it without the secret key. However, the secret token is limited to one Secure Shell session. If the other side has not received and decrypted the message in that time, a new key must be created to keep the process secure.
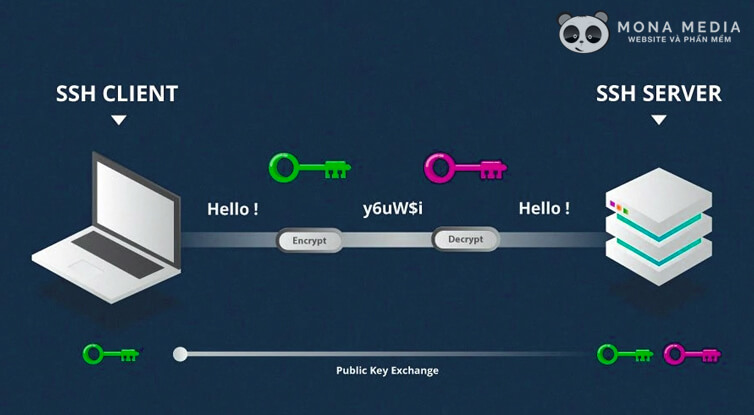
Asymmetric encryption uses two separate keys for encrypting and decrypting. The public key is shared with all parties involved, while the private key is always kept secret. The two keys are closely related and depend on each other, so a message cannot be decrypted by knowing only one of them.
However, asymmetric encryption cannot be applied to every Secure Shell operation. The public-private key pair also has a limited usage time. As soon as decryption succeeds, the Secure Shell session begins.
Hashing is also a common encryption method in the Secure Shell protocol. A hash is simple to create from a single input, but the original input cannot be recovered from the hash. Put simply, the client holds the input, and only the client can produce a cryptographic value that lets both sides enter the input. Secure Shell uses hashing to verify messages, so that commands cannot be forged by any method.
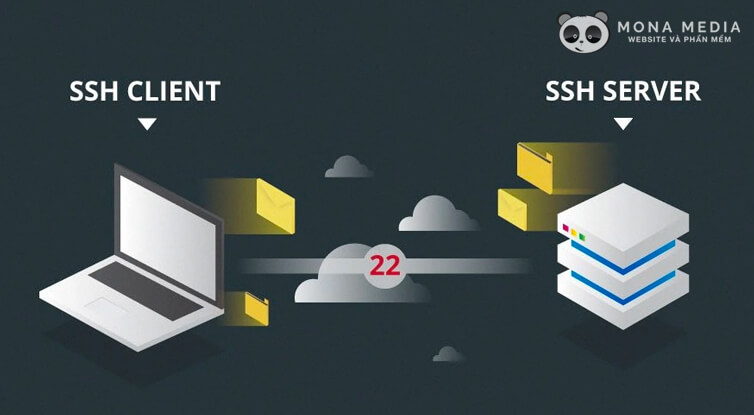
There are two basic stages in the SSH protocol's encryption handling: negotiating the encryption standard and authentication. When the client connects over TCP, the server returns the versions it supports. If the client also has a matching Protocol version, an agreement is made and the connection continues. The server uses a key that only the client can use to verify the information correctly.
After the connection is set up, both sides use the Diffie-Hellman key exchange algorithm to create a symmetric key. This algorithm lets the server and client share a key for communication; both sides agree to encrypt and can create a symmetric key for the whole Secure Shell session. Once the encrypted session is established, the protocol moves on to user authentication.
Users are granted access to the Web Server if the protocol can authenticate the information between the two devices. You enter a username and password, which are sent safely through the symmetric secure tunnel. For more safety, though, you should use Secure Shell key pairs, a smart set of keys that can authenticate users without a password.
The SSH protocol, along with the SSL/TLS protocol and Telnet, all provide authentication between parties. Telnet is one of the earliest Internet protocols, while HTTPS can be seen as the full version of Secure Shell. All three share similar features; see the table below to understand them better.
| Comparison criteria | SSH | SSL/TLS | Telnet |
| Port it runs on | Port 22 | Port 22 | Port 23 |
| Security | Very secure | Less secure | Less secure |
| Encryption mechanism | Public Key | Public Key | Plain text transmission |
| Suitable systems | Public Network | Public Network | Private Network |
| Compatible operating systems | All operating systems | All operating systems | Linux and Windows |
| Functionality | Remote server control and management, linking workstations and clients | Remote server control and management | Remote server control and management |
SSH is highly regarded for security, but some issues remain. For example, keys pile up on the client and need IT staff to manage and clean them out. Data stored in Secure Shell files can also be abused to take over authenticated access. Businesses therefore need stricter storage procedures.
That covers Secure Shell, how it works and its encryption techniques. It is a powerful tool for controlling and managing servers remotely. We hope this article has answered what SSH is and given you the related information.

CEO & Founder · The MONA
Founder of The MONA, who built a services company of 60+ staff with 14,000+ projects delivered. Khánh Hùng shares how he thinks about building systems that run themselves, automating a business, and the real lessons from delivering projects at MONA.
 1,5K




Professional website
design services
Own a website with a beautiful, 100% exclusive design and a lifetime warranty, with the ability
to expand features flexibly as your business grows, starting today!






 MONA will never sell your information or send you spam


 MONA will never sell your information or send you spam
